Use a remote proxy to access data objects
The remote proxy allows you to connect to another PingIDM instance or Advanced Identity Cloud tenant to access data objects as if they are local resources. Through the /openidm/external/idm/<remote-instance-name> endpoint, you can:
-
Query and manage users on a remote instance
-
Create sync mappings between instances
-
Run scripts that interact with remote data
-
Perform reconciliation to sync data across environments
Common use cases
-
Environment promotion: Sync data from sandbox → staging → production.
-
Geographic distribution: Keep geographically distributed data centers in sync.
-
Migration: Sync data between self-managed PingIDM instances and Advanced Identity Cloud tenants.
-
Multi-instance management: Manage multiple PingIDM instances or Advanced Identity Cloud tenants from a single control plane.
| The proxy doesn’t support liveSync or implicit sync from remote resources. You must use reconciliation when pulling data from a remote system. |
High-level setup
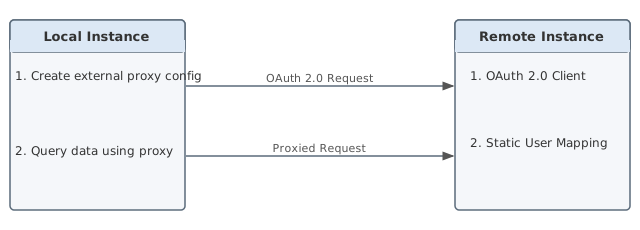
Setting up a remote proxy involves configuring both a local instance (where you configure the proxy) and a remote instance (where the proxy points).
Local instance:
-
Create an external proxy configuration pointing to the remote instance.
-
Configure OAuth 2.0 client credentials for authentication.
Remote instance:
If the remote instance is fronted by PingAM:
-
Create an OAuth 2.0 client with the
client_credentialsgrant type. -
Configure a static user mapping that grants the OAuth 2.0 client only the roles required for the proxy use case (for example,
internal/role/platform-provisioning). -
Ensure the OAuth 2.0 client has the
fr:idm:*scope.
Setup overview:
Prerequisites
For the local instance, you need:
-
Instance hostname
-
For example:
https://<local-instance-fqdn>
-
-
Credentials for authentication
-
OAuth 2.0 client ID from the remote instance (for example,
<clientIDName>) -
OAuth 2.0 client secret from the remote instance
-
Realm name on the remote instance, if the remote instance is fronted by PingAM (for example,
alphaorbravo)
For the remote instance, you need:
-
Instance hostname
-
For example:
https://<remote-instance-fqdn>
-
-
Credentials for authentication
-
Realm name, if the remote instance is fronted by PingAM (for example,
alphaorbravo) -
OAuth 2.0 client ID (for example,
<clientIDName>) -
OAuth 2.0 client secret
SSL/TLS certificates
To connect to a remote instance over SSL or TLS, you must import the remote instance’s server certificate into your local instance’s truststore. This is only necessary if a CA that isn’t already in the truststore signed the certificate. Learn more in CA-signed certificates.