Audit parameters
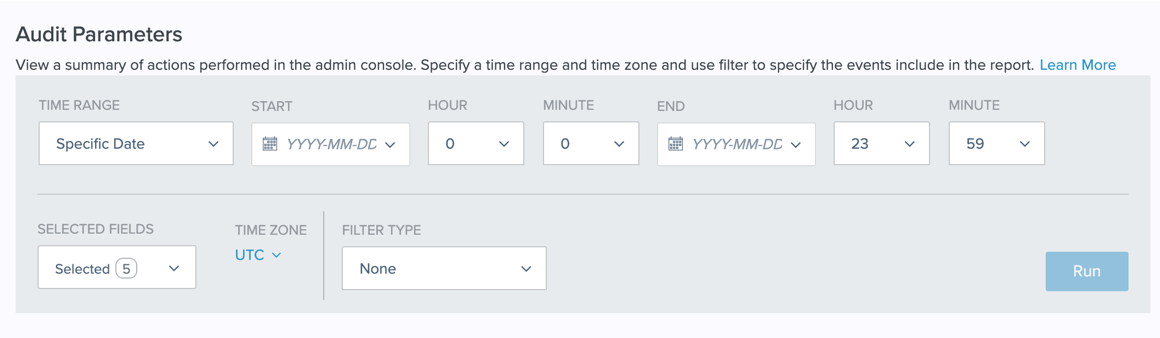
Use audit parameters to specify the details of your search results.
Time Range
Limit the report results to a specific time period.
|
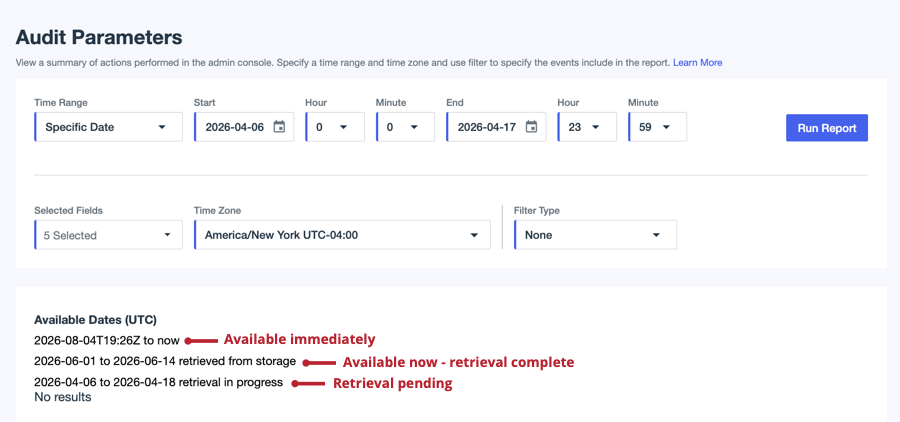
Data up to 14 days old relative to the current date is available immediately. Data older than 14 days must be requested from the Audit page or using the API. You can’t request data for dates that are more than 2 years (730 days) before the current date. Depending on the number of days requested and the average number of events logged per day, the retrieval process can take from 2 to 24 hours. You can request a maximum of 14 days of data from within the data retention period, and you can’t request additional data while another request is pending. If you have a valid email address in PingOne, you’ll be notified when the requested data is available. At that point, you can return to the Audit Parameters page and run queries against the data for the timeframe requested. The retrieved data is available for 14 days from the date of the retrieval request. |
| Option | Description |
|---|---|
Relative |
A time range relative to the current time. In the Within fields, select a number and a time period. For example, 2 and weeks. |
Specific Date |
A time range with a specified start and end date, such as “March 27 to April 10.” Optionally, you can also include the time of day using the Hour and Minute fields for the start and end dates. |
|
If you enter a time range more than 2 years (730 days) from the current date, you’re prompted to adjust the time range before submitting the request. |
Selected Fields
Specify which fields appear in the results list.
| Option | Description |
|---|---|
Timestamp |
Shows the date and time of the event. The format is: |
Event Type |
Shows the type of event returned. You can find a complete list of events logged in PingOne in Audit Reporting Events in the PingOne API documentation. |
Description |
Shows a brief description of the event. |
Client |
Shows the name of the application or OAuth client that performed the event. |
User Identity |
Shows the user who performed the action. |
Population |
Shows the population of the resource on which the event was performed. |
Resource Type |
Shows the type of resource affected by the event, such as an application, identity provider, or digital wallet. |
Filter Type
Limit the search results based on the specified filters.
| Option | Description |
|---|---|
Resource ID |
Find activities that were performed on a specific resource, identified by its resource ID (UUID). For PingOne DaVinci events, enter a flow ID, variable ID, connector instance ID, flow policy ID, application ID, or UI template ID to scope results to a specific DaVinci resource. |
Correlation ID |
Find activities by correlation ID. When an HTTP request is received, it’s assigned a correlation ID. You can use the correlation ID to associate HTTP responses with messages in the event log. |
Event Type |
Find activities by event type. You can find a complete list of events logged in PingOne in Audit Reporting Events in the PingOne API documentation. |
User ID (Actor) |
Find activities performed by a specific user, identified by user ID. User IDs are immutable, so this filter provides a stable way to identify the user over time. If they change their username, you can still find the activities performed by that user. |
User Name (Actor) |
Find activities performed by a specific user, identified by username. Because usernames can change, results might not refer to the same person over time. Use User ID (Actor) if you need a stable identifier. |
Client (Actor) |
Find activities performed by a specific OAuth client acting as the caller, such as the PingOne admin console ( |
Resource Population |
Find activities performed on resources in one or more populations, matched by the population ID associated with the target resource. Use this filter to return everything that happened to users in a given population. This filter differs from the Population filter, which only matches activities performed on a specific population object. |
Resource Type |
Find activities performed on a specific type of resource, such as an application, identity provider, or digital wallet. This filter returns all activities whose target resource is the selected type, regardless of which specific resource was affected. |
Population |
Find activities performed on a specific population object itself, such as when the population was created, updated, or deleted. This filter doesn’t include activities performed on users in that population. Use Resource Population for that use case. |
User |
Find activities performed on a specific user, identified by user ID (not by the username), such as updates to that user’s profile, password, or credentials. This filter differs from User ID (Actor), which matches activities performed by that user. |
Application |
Find activities performed on a specific application resource, such as when the application was created, updated, or deleted. Enter an application ID or name. This filter differs from Client (Actor), which matches activities performed by an application acting as the caller. |