Setting up SSO to PingFederate
To set up single sign-on (SSO) access for administrators from the PingOne admin console to the PingFederate administrative console, configure PingOne and PingFederate and test the sign-on experience.
Before you begin
Ensure that you have:
-
A licensed version of PingFederate 10.1.2 or later
-
A PingOne account
-
A text editor or terminal
-
The Environment Admin role assigned in PingOne
|
For PingOne users to use SSO to PingFederate, they must have one or more PingFederate-related roles in PingOne. You can assign roles in the PingOne admin console. Learn more in Administrator Roles and Managing user roles. |
Adding PingFederate to an environment
Add PingFederate to your existing PingOne environment.
Steps
-
In the PingOne admin console sidebar, click the Ping Identity logo to open the Environments page and browse or search for the applicable environment.
-
On the Environments page, click the environment to open the details panel.
-
Click Manage Environment and click Overview in the sidebar.
-
In the Environment Capabilities section, click the Plus icon ().
-
Click Add next to PingFederate and any other products or services that you want to add to the environment.
-
Click Finish.
Configuring SSO to PingFederate
After adding PingFederate to your environment, configure SSO from the PingOne admin console.
Steps
-
In the PingOne admin console, go to the Overview page and locate the PingFederate entry in the Optional Connections section.
-
Click the More Options icon () and then click Configure.
-
Enter the URL for the PingFederate administrative console.
Example:
https://<pf_host>:<pf_port>/pingfederate/app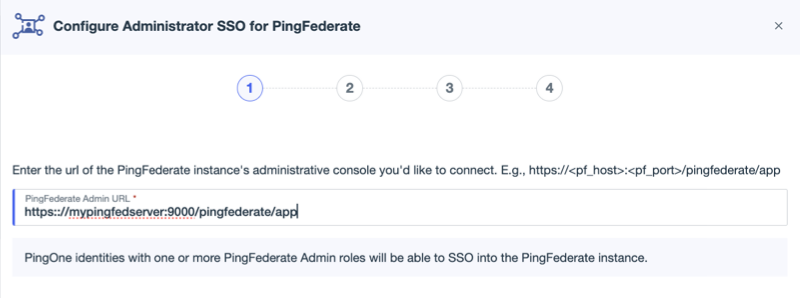
-
Click Save and Continue.
-
Copy the provided OpenID Connect (OIDC) settings to the
oidc.propertiesfile on the PingFederate administrative server.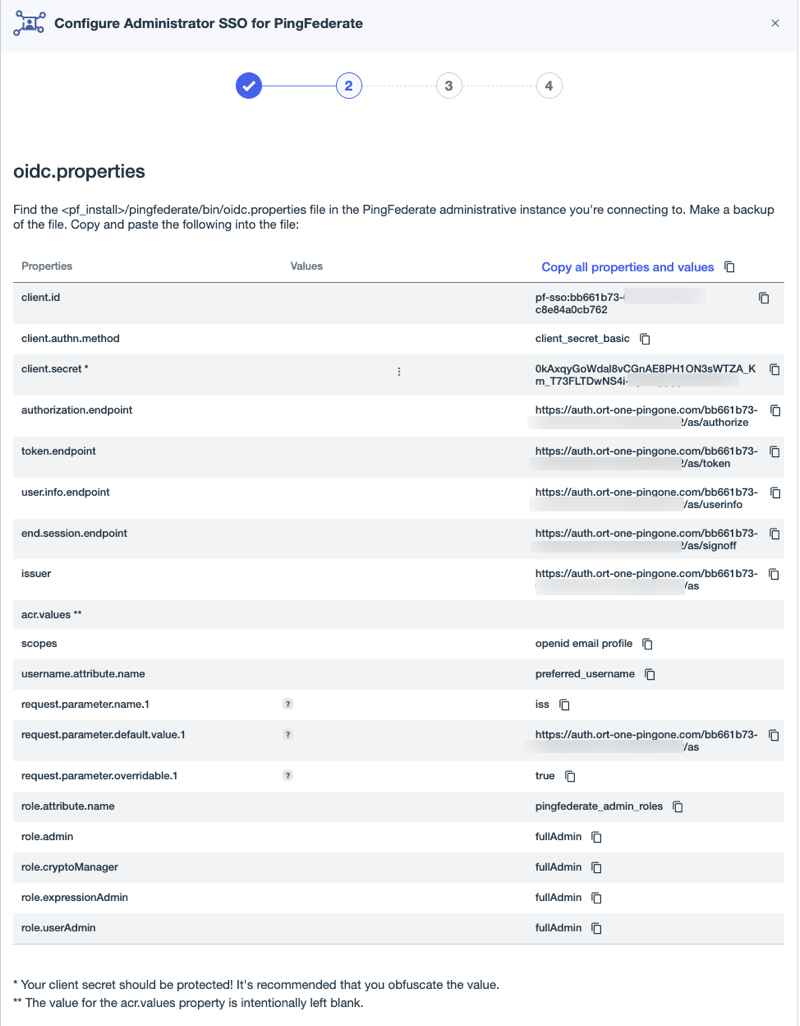
The following three unique parameters allow administrators to use SSO into PingFederate 11.2 or later from any PingOne environment if they have the proper administrator roles assigned for the environment. Learn more in Administrator Roles.
For PingFederate 11.1 or earlier, the administrator’s identity must exist in the same PingOne environment as the SSO configuration, and these parameters can’t be used.
Request Parameter Value request.parameter.name.1The request parameter’s name. The value is
iss.This field is required. Do not use URL encoding for the name.
request.parameter.default.value.1The default value of the request parameter. The value is the authorization endpoint of the current environment if the administrator identity resides in the current environment.
-
If this parameter isn’t included in the request, the default value is included in the authorization request.
-
If this parameter isn’t included in the request, and no default value is specified, the parameter isn’t included in the authorization request.
-
This field is optional when
request.parameter.overridable.1is set totrue.
request.parameter.overridable.1Specifies whether the request parameter can be overridden at runtime. The value is set to
true, which allows the administrator identity’s home environment to override the value.This field is optional. Possible values are
trueorfalse. If not specified, the default isfalse.If this property is set to
false, therequest.parameter.default.value.1is always included in the authorization request and can’t be overridden. -
-
Click Next.
-
Copy the provided
run.propertiesfile attribute value to therun.propertiesfile on the PingFederate administrative server.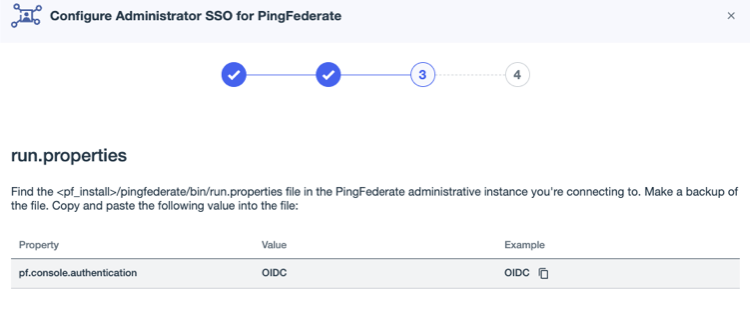
-
Click Next and then click Close.
-
Restart the PingFederate server.
Testing SSO to PingFederate
After configuring PingOne and PingFederate, test the sign-on experience to PingFederate.
Before you begin
You must have a PingFederate-related role to perform this task. Learn more in Administrator Roles.
Steps
-
Go to the Overview page for the environment and click the PingFederate entry in the Optional Connections section.
Result:
The PingFederate administrative console opens.