SDG

Overview of the SP SSO flow

With the SDG CTS Integration Kit, PingFederate allows a service provider (SP) to start a SDG session with user attributes from the identity provider (IdP).

The following figure illustrates an IdP-initiated single sign-on (SSO) scenario where PingFederate uses the SDG CTS SP Adapter to parse an assertion and create an SDG session cookie.
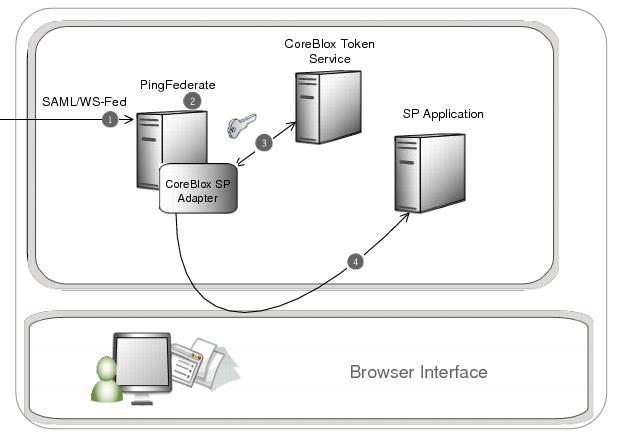
A diagram showing an example SSO flow using the SDG CTS SP Adapter and the CTS.

Description

  1. The PingFederate SP server receives an assertion from the IdP.

  2. PingFederate parses the assertion.

  3. The SDG CTS SP Adapter uses the user attributes to create and authorize a session with the CTS.

  4. The adapter redirects the browser with a request that contains the session cookie.